برچسب: Digital Forensic


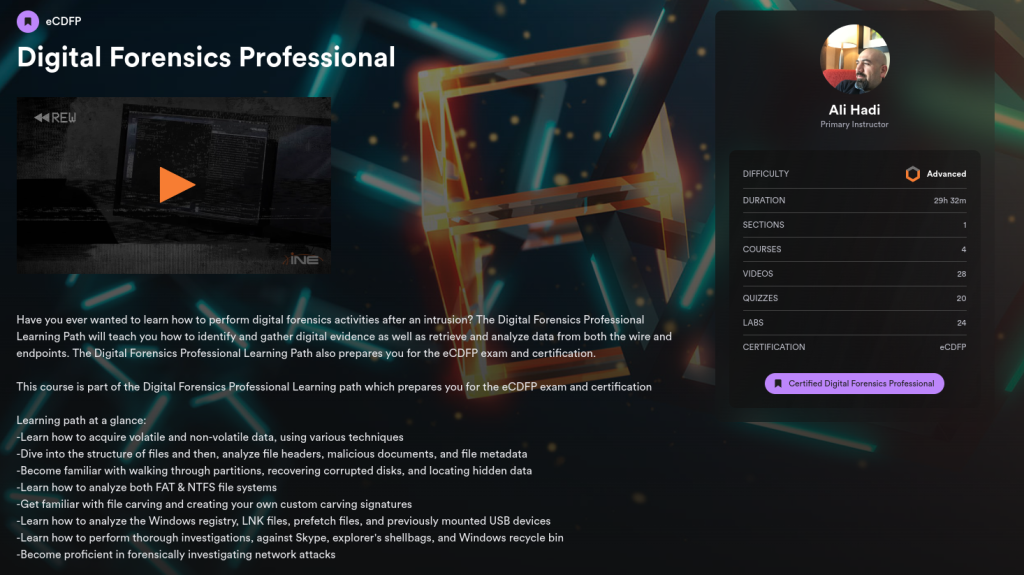
Have you ever wanted to learn how to perform digital forensics activities after an intrusion? The Digital Forensics Professional Learning Path will teach you how to identify and gather digital evidence as well as retrieve and analyze data from both the wire and endpoints. The Digital Forensics Professional Learning Path also prepares you for the eCDFP exam and certification.

This course is part of the Digital Forensics Professional Learning path which prepares you for the

eCDFP exam and certification

دانلود دوره

Incident response to live cyberattacks requires silent navigation through compromised assets, sometimes in large distributed networks. The popular approach relies on EDR or other live agent-based solutions. However, the activation of security agents and obvious activities on live compromised systems may trigger alerts of advanced threat actors. Once alerted, a cleanup operation and destruction of evidence can happen. Moreover, offline system analysis may not be easy due to the physical distance to the compromised system or scale of the network. This is where remote stealthy threat discovery with “scoutware”, software for threat hunting and instant system analysis, becomes incredibly useful.

In our training you will be introduced to the free, open-source scoutware tool Bitscout developed by Vitaly Kamluk from Kaspersky GReAT in collaboration with INTERPOL, that has been successfully used by Kaspersky researchers for years. The cases demonstrated in the training were developed by Vitaly Kamluk and Nicolas Collery, Executive Director at DBS Bank, primary incident responder. During the training you will create your own remote analysis tool and practice it right away in the provided virtual lab!

دانلود دوره

Digital forensics and incident response are two of the most critical fields in all of information security. The staggering number of reported breaches in the last several years has shown that the ability to rapidly respond to attacks is a vital capability for all organizations. Unfortunately, the standard IT staff member is simply unable to effectively respond to security incidents. Successful handling of these situations requires specific training in a number of deeply technical areas including file systems, operating system design, and knowledge of possible network and host attack vectors.  During this training, students will learn how to approach digital investigations in a manner that allows for immediate forensic exploitation of relevant data both in-memory and on-disk. Significant hands-on experience during labs will train students to analyze the same types of evidence and situations that they will encounter in real-world investigations. This class is structured so that a specific analysis technique is discussed and then the students immediately analyze staged evidence using their newly gained knowledge. Not only does this approach reinforce the material learned, but it also gives students a number of new skills as the course proceeds. Upon completion of the training, students will be able to effectively analyze a large number of digital evidence sources, including both on-disk and in-memory data, using the latest and most effective forensics tools and techniques. These skills will be immediately usable in a number of investigative scenarios and will greatly enhance even experienced investigators’ skillset. Students will also leave with media that contains all the tools and resources used throughout the training.

دانلود دوره

Digital Forensics is defined as the process of preservation, identification, extraction, and documentation of computer evidence which can be used by the court of law. It is a science of finding evidence from digital media like a computer, mobile phone, server, or network. A digital forensic analyst exploits digital evidence and investigates computer security incidents to derive useful information in support of system/network vulnerability mitigation.

دانلود دوره

Digital forensics is now back in focus with the rapid increase in cybercrimes. In this course, Digital Forensics: Getting Started, you’ll learn the skills required to conduct a digital forensics investigation from acquisition to the analysis phase. First, you’ll discover the process of hypothesis testing by applying forensic science techniques to digital forensics. Next, you’ll explore how to overcome the challenges of digital evidence by using evidence integrity methods such as write blockers and verifying hashes. Finally, you’ll learn how to examine the Windows Registry files and create a timeline of events for your case. When you’re finished with this course, you’ll have a foundational understanding of the digital forensics domain that will help you conduct successful cybercrime investigations.

دانلود دوره

The Enterprise Forensics and Response course is designed to provide students with both an investigative construct and techniques that allow them to scale incident response activities in an enterprise environment. The focus of the lecture portion of the course work is understanding the incident investigation process, objective oriented analysis and response, intrusion analysis and an exploration of attacker Tactics and Techniques. The technical portion of the course will focus on how to conduct incident investigations at enterprise scale using the remote evidence acquisition and analysis tool Velociraptor along with other free and open-source tools. The focus of the technical portion will be on extracting usable Indicators of Compromise (IOCs) related to specific MITRE ATT&CK tactics. For example, students will be instructed on extracting and analyzing evidence related to the Execution TA0002 of malicious code or LOLBAS. From here, they will be tasked with addressing containment and eradication measures. This course will combine technical elements along with lecture that provides students with both an investigative construct and techniques that allows them to analyze evidence and provide stakeholders with data necessary to limit the damage of modern cyber-attacks.

Antisyphon: Enterprise Forensics and Response

دانلود دوره