 Security Education
 OffSec
 iNE
 Antisyphon
 EC-Council
 Applied Network Defense
 Kaspersky
 Sektor7
 CompTIA
 TCM Security
 BlackHat
 13Cubed
 Dark Vortex
 Enciphers
 Forty North
 Cyber warfare Labs
 Maltrak
 Scorpio Software
 Security Onion
 Zero Point Security
 SentinelOne
 Altered Security
 SpecterOps
 Pentester Academy
 CQURE
 PluralSight
 StationX
 Cybr
 موسسههای دیگر
The course will purely focus on Web/Server/Mobile offensive hacking using the Bug Bounty Hunter Mentality.
The course will purely focus on Web/Server/Mobile offensive hacking using the Bug Bounty Hunter Mentality.
The RTFM Video Library is an invaluable resource for serious Red Team members who find themselves on critical missions. Led by a seasoned Red Team operator, this high-quality video series delves into various aspects of offensive security, providing practical guidance and insights.
1: Infrastructure Setup
2: Initial Access
3: Situational Awareness
4: User Level Persistence
5: Escalation
6: Lateral Movement
7: Active Directory Enumeration
8: Domain Fortification
9: Hunting for User Workstations
10: Active Directory Forest Compromise
11: Secret Enclave Compromise
12: Pivoting through Tunnels
Many publications exist documenting ways to attack Wi-Fi networks. Still, the gap between old methods that have become obsolete and the current state and outdated tools can be frustrating for someone who wants to learn or even update his knowledge in this field. This course aims to learn the modern ways of assessing the security of Wi-Fi networks and how to apply these attacks against organizations during a Red Team engagement. Indeed, during this course, we will be able to start from the very beginning by talking about old, current, and new attacks and opportunities to allow attendees to fulfill their pentest or Red Team engagements in the future based on our recent experiences.
Introduction
Network introspection
Attacks and risks
Completion
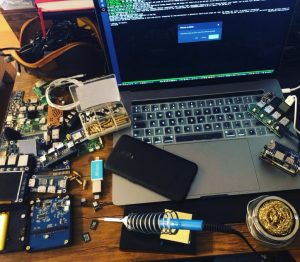
The topic of Hardware Hacking is one of the topics that is rarely addressed and mentioned in official courses, but nevertheless it is one of the most important techniques required for hackers who intend to carry out field and physical attacks. This package includes videos from conferences like DefCon on this topic, hands-on courses, lots of books, YouTube videos and blogs. In this course, you will learn a wide range of topics such as making (Rubber Ducky) BAD USB, FPGA attacks, security testing of switches and routers, Wifi jamming, direct attacks on Memory, attacks on Mouse, etc. This package includes more than 40 hours of educational videos and many books. To know the names of the courses and books in this package, you can watch the video of this article.
BTL1 is designed to train technical defenders who can defend networks and respond to real-world cyber incidents. The skills and tools you learn apply directly to security roles and are used by defenders worldwide.
Reversing Hero course is a very good course for people who want to learn reverse engineering from beginner to intermediate level. This course consists of 12 hours of video, the degree of difficulty of which increases step by step, and also in the Reversing Hero course, you have to try to solve the given exercises by yourself, and if you are completely stuck, you can watch the video of the solution to the exercise.